WoW Reverse Engineering Notes — Sept 6, 2016 (working through "Reversing: Secrets of Reverse Engineering")
Found sfc.dll loaded in memory - was curious about what it is. First time doing something like this...
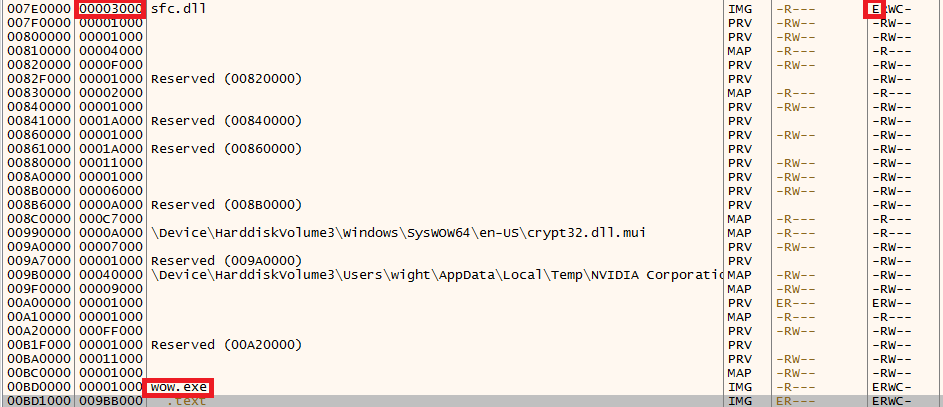
- Dumped memory using x32dbg
- Windows DLL
- Purpose? Windows file protection
- More info - some exported functions I have are not listed: somewhat scary is the connectToServer and InitiateScan but then again I could see this being apart of the functionality. Scan a file to verify it isn't corrupted and check signatures remotely...
- http://www.nirsoft.net/dll_information/windows8/sfc_dll.html
- Interesting discussion here: http://answers.microsoft.com/en-us/windows/forum/windows_vista-update/sfcdll-error-message/34dddcae-c392-4cea-9be2-d1a2a78d39ee
- Opened in 010 Editor found exported functions? some examples:
-
- SRSetRestorePoint
- SRSetRestorePointA
- SfcClose
- SfcConnectToServer
- SfcFileException (an example of something not listed in x32dbg but is found in 010 editor - makes me feel better about SfcConnectToServer and SfcInitiateScan not being found in x32dbg
- SfcGetNextProtectedFile
- SfcInitiateScan
- Via x32dbg
-
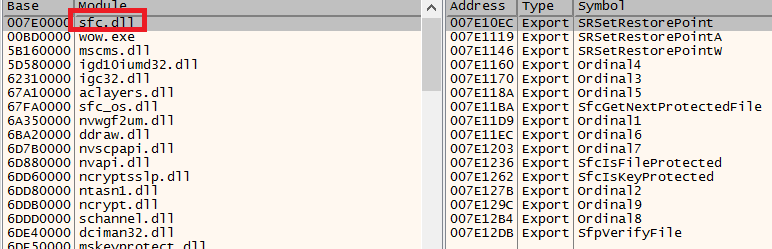
- interesting how some of the ones found in 010 editor aren't listed. maybe they aren't exports?
-
- Dumped memory for that file
- Is loaded before WoW.exe in memory
- Is executable